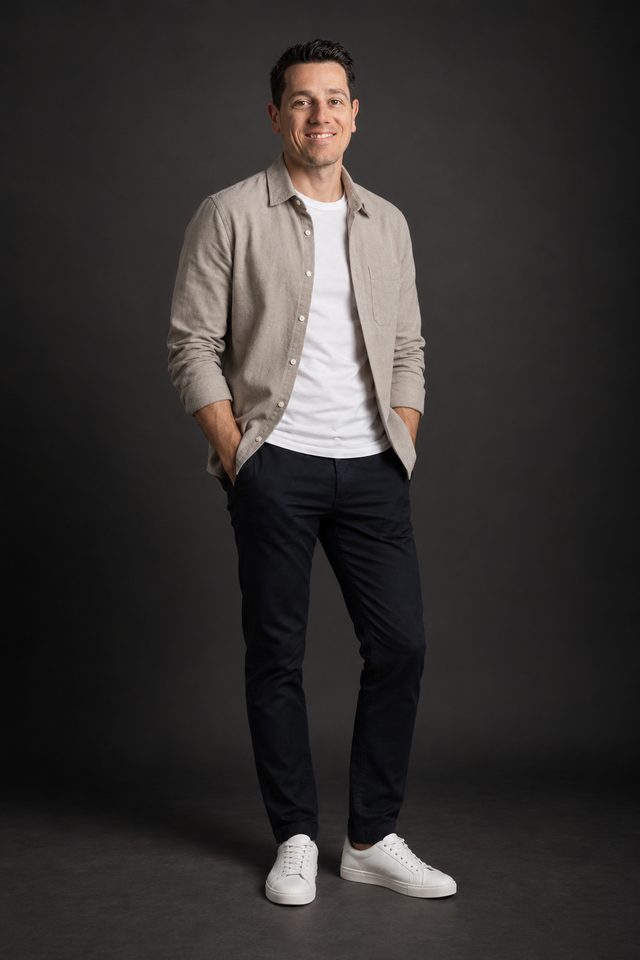
Yerko Marcić

Information Risk & Assurance · Regulated financial services

I make technology risks visible to the organisation and advise on the controls that reduce them.

More than five years in the Netherlands, at Atos and, through FDM Group, at Shell and Shell Asset Management Company. Most of my work sits where technology risk meets someone from outside who is going to verify it: an auditor, or a client's security team.

  • 15+information risk assessments and business impact analyses led
  • 52findings, policy exceptions and vulnerabilities managed end to end
  • 3ISAE 3402 controls executed and evidenced, with no deviations
  • 2IT controls implemented after the assessment of a new data platform

Selected work

Five pieces of work, and what came out of each.

SWIFT CSP 2025 attestation

Shell Asset Management Company · The Hague · via FDM Group

  • SWIFT CSP
  • SOC 2 Type II
Situation
The 2025 SWIFT Customer Security Programme attestation had to be submitted, with the evidence spread across four to five owners.
What I did
Led the delivery end to end. I collected the evidence from each owner, ensured it fulfilled the control requirements, and reviewed the supplier's SOC 2 Type II report.
Outcome
Submitted on time.

ISAE 3402 controls

Shell Asset Management Company · The Hague · via FDM Group

  • ISAE 3402
Situation
Three of the controls in the annual ISAE 3402 report were mine to run.
What I did
Executed the three controls and produced the supporting evidence, working alongside the external auditors.
Outcome
Closed with no deviations.

Assessment of a new data platform

Shell Asset Management Company · The Hague · via FDM Group

  • Information risk assessment
  • IT controls
Situation
A new enterprise data platform was fed by several applications that had already been assessed.
What I did
Assessed the platform itself.
Outcome
Two IT controls were implemented as a result, user access management and audit logging, so that an incident can be traced back.

Rebuilding a contract baseline

Atos · Amstelveen · clients: Univé and VGZ

  • Security services
  • Documentation
Situation
Two contracts were up for renewal and nothing had been documented.
What I did
Rebuilt the baseline from invoicing evidence, close to forensic work: cross-checking the contract manager's figures against what the security architect was actually maintaining. Delivered against a pre-Christmas deadline.
Outcome
Two additional services were added after asking what the client needed now. The documentation was left future-proof for whoever came next.

Third-party risk management

Shell Asset Management Company · The Hague · via FDM Group

  • Security assurance
  • SOC 2 Type II
Situation
The business needed to assess suppliers' security posture during onboarding and monitor whether their controls remained appropriate throughout the relationship.
What I did
Reviewed supporting evidence and independent assurance reports, such as SOC 2 Type II reports, to assess suppliers' security controls. Identified gaps, clarified findings with suppliers, and communicated risks and recommended actions to internal stakeholders as part of onboarding and ongoing monitoring.
Outcome
Supported informed supplier onboarding decisions and ongoing visibility into third-party security risks, helping stakeholders prioritise areas requiring follow-up.

Also at Shell Asset Management Company: support for DORA readiness through ICT risk management and operational resilience activities.

How I work

One risk, in clear terms for engineers and for management.

I work with two audiences: the engineers who implement the mitigation, and the management that approves it.

One findingA new data platform, fed by applications that were already assessed.

For the engineers

The platform itself has no user access management and no audit logging. Both controls need to be implemented there.

For management

If there is an incident on this platform, we cannot trace back what happened. Two controls close that gap.

And after the finding

My work does not stop at identifying a risk: I challenge remediation where needed, explore alternative approaches, and help stakeholders reach solutions that address the risk while remaining practical for the business.

Background

I did not come from IT.

In 2020 a manager in the Netherlands gave me six months to learn cybersecurity from zero: if I learned, I stayed. I stayed more than five years.

I studied business administration in Chile. I have been in the position of not knowing and having to deliver anyway, and I know what it takes.

Yerko Marcić, standing
  1. Business Administration and ManagementPontificia Universidad Católica de Valparaíso, Chile
  2. Business Analyst · EvalueserveViña del Mar, Chile · model risk management
  3. Cybersecurity Consultant · AtosAmstelveen · Security Solution Advisory & Pre-SalesSix months to learn it from zero.
  4. IT Security & Compliance Analyst · ShellThe Hague · employed by FDM Group
  5. Information Risk Management Analyst · Shell Asset Management CompanyThe Hague · employed by FDM Group

Credentials

What I have worked with, and what I only know.

Frameworks and standards
Worked withDORA · COBIT (through the Shell IT Control Framework) · SOC 2 · ISAE 3402
Knowledge levelISO/IEC 27001 · NIST CSF 2.0
Certifications
ISO/IEC 27001:2022 Foundation
Business Analysis Foundation
In preparationAI Governance and Compliance
Education
Bachelor's degree in Business Administration and Management (Ingeniería Comercial)Pontificia Universidad Católica de Valparaíso, Chile
Languages
SpanishNative
EnglishFluent
PortugueseIntermediate
DutchBasic

Contact

If one of these cases is close to what you need, write to me.